Enterprise Identity and Access Management deployments have never been more strategically important, or more technically demanding. As organizations move deeper into hybrid cloud environments, adopt Zero Trust frameworks, and consolidate identity sprawl inherited from years of organic growth, the pressure to deploy reliable, scalable IAM infrastructure quickly has intensified considerably. Yet the reality on the […]
Financial institutions operate in one of the most targeted environments in the world. Banks, credit unions, insurance carriers, and investment firms hold vast amounts of sensitive data, process millions of transactions daily, and manage access for tens of thousands of employees, contractors, and customers at any given time. The attack surface has never been larger, […]
Passwords have been guarding digital accounts since the earliest days of computing. Despite decades of technological progress, they remain the most common authentication method in use today, and the most frequently exploited. According to the Verizon Data Breach Investigations Report, stolen or compromised credentials are involved in over 80% of confirmed data breaches. That single […]
Every major data breach in recent memory has one thing in common: compromised credentials. Whether it was a phishing email, a brute force attack, or a leaked password database, the entry point was almost always an identity. Passwords remain the most widely used authentication mechanism in the world, and that makes them the most targeted. […]
One-Time Password (OTP) authentication is a security mechanism that generates a unique, temporary passcode valid for a single login session or transaction. Unlike static passwords, OTPs expire after use or within a short time window, making stolen credentials nearly useless to attackers. OTP is a foundational component of multi-factor authentication, enterprise IAM, and modern Zero […]
Customer relationships drive revenue. The systems that manage those relationships are now a top target for attackers, a compliance obligation for regulators, and a strategic lever for growth. Cloud CRM sits at the intersection of all three, which is why organizations from mid-market companies to global enterprises are making the shift, and why getting it […]
Every major data breach in recent memory shares a common thread: compromised identities. Whether attackers exploit stolen credentials, abuse excessive privileges, or move laterally through enterprise environments using legitimate access, identity has become the primary attack vector in modern cybersecurity. The traditional network perimeter no longer holds. Firewalls and VPNs cannot protect what attackers are […]
Mobile devices are now the primary access point for enterprise resources. Employees check email on personal iPhones, approve workflows from tablets during travel, and connect to cloud applications from home networks they share with smart TVs and gaming consoles. That shift happened fast, and most organizations are still catching up on the security side. Mobile […]
In Short: Cybersecurity threats to businesses are malicious activities or system vulnerabilities that attackers exploit to gain unauthorized access, steal data, disrupt operations, or extort organizations. Common threats include phishing, ransomware, insider attacks, and supply chain compromises, each carrying significant financial, legal, and reputational consequences for enterprises. Cybercrime now costs the global economy over $8 […]
Why Is IAM Important? Identity and Access Management (IAM) is important because it controls who can access your systems, data, and applications and what they can do once they get in. Without IAM, organizations face data breaches, compliance failures, and insider threats. A strong IAM strategy reduces risk, supports regulatory requirements, and keeps sensitive information […]
Healthcare organizations are under more pressure than ever. Cyberattacks targeting hospitals and health systems have surged over the past several years, with breaches exposing millions of patient records annually. At the same time, regulatory requirements keep expanding, digital care delivery is accelerating, and the workforce managing sensitive clinical systems grows more complex every year. At […]
Every organization today faces a version of the same problem. The workforce is distributed, the cloud environment is complex, and the number of applications employees need to access keeps growing. At the same time, regulators are demanding stricter controls, cyber threats are increasing in frequency and sophistication, and IT teams are stretched thin managing access […]
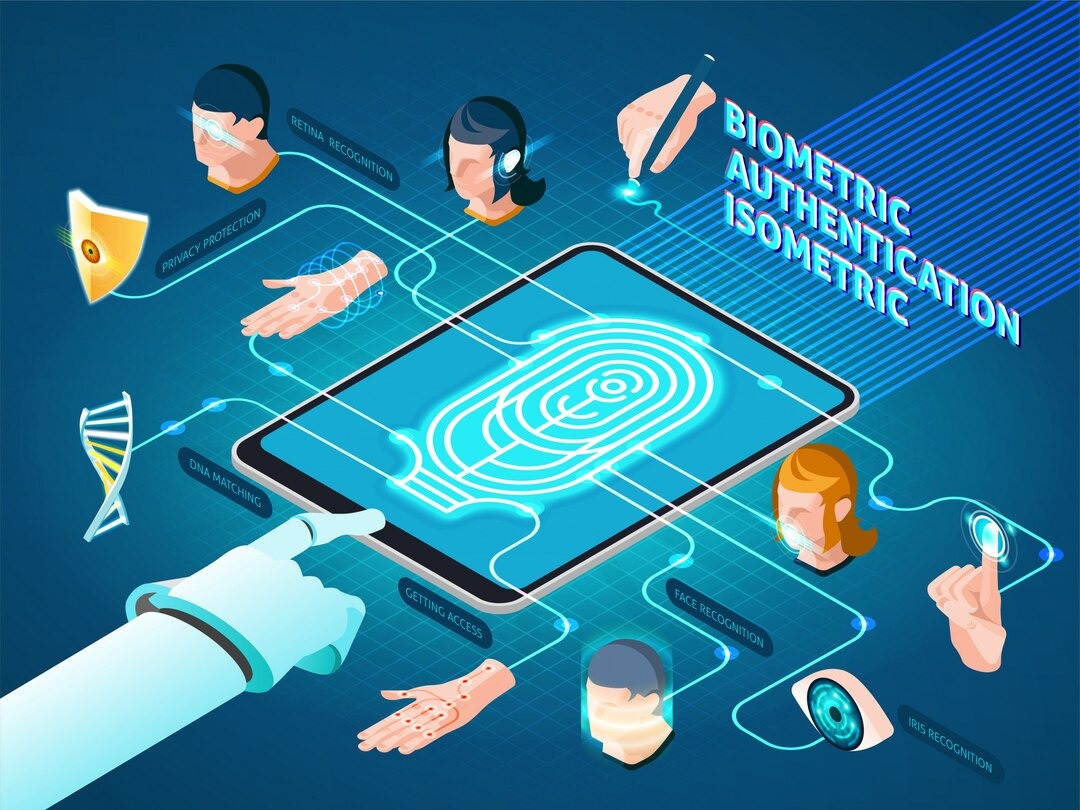
Healthcare organizations face a reality that most industries never have to confront: a single security breach can simultaneously expose millions of patient records, trigger federal investigations, result in multi-million dollar fines, and erode the patient trust that clinical operations depend on. In 2023 alone, healthcare data breaches affected over 133 million individuals in the United […]
Every CISO has been in that meeting. Leadership wants to know why the organization should spend hundreds of thousands of dollars on Identity and Access Management, and the security team struggles to put a hard dollar figure on it. Unlike a new server or a revenue-generating SaaS tool, IAM doesn’t produce revenue directly. It prevents […]
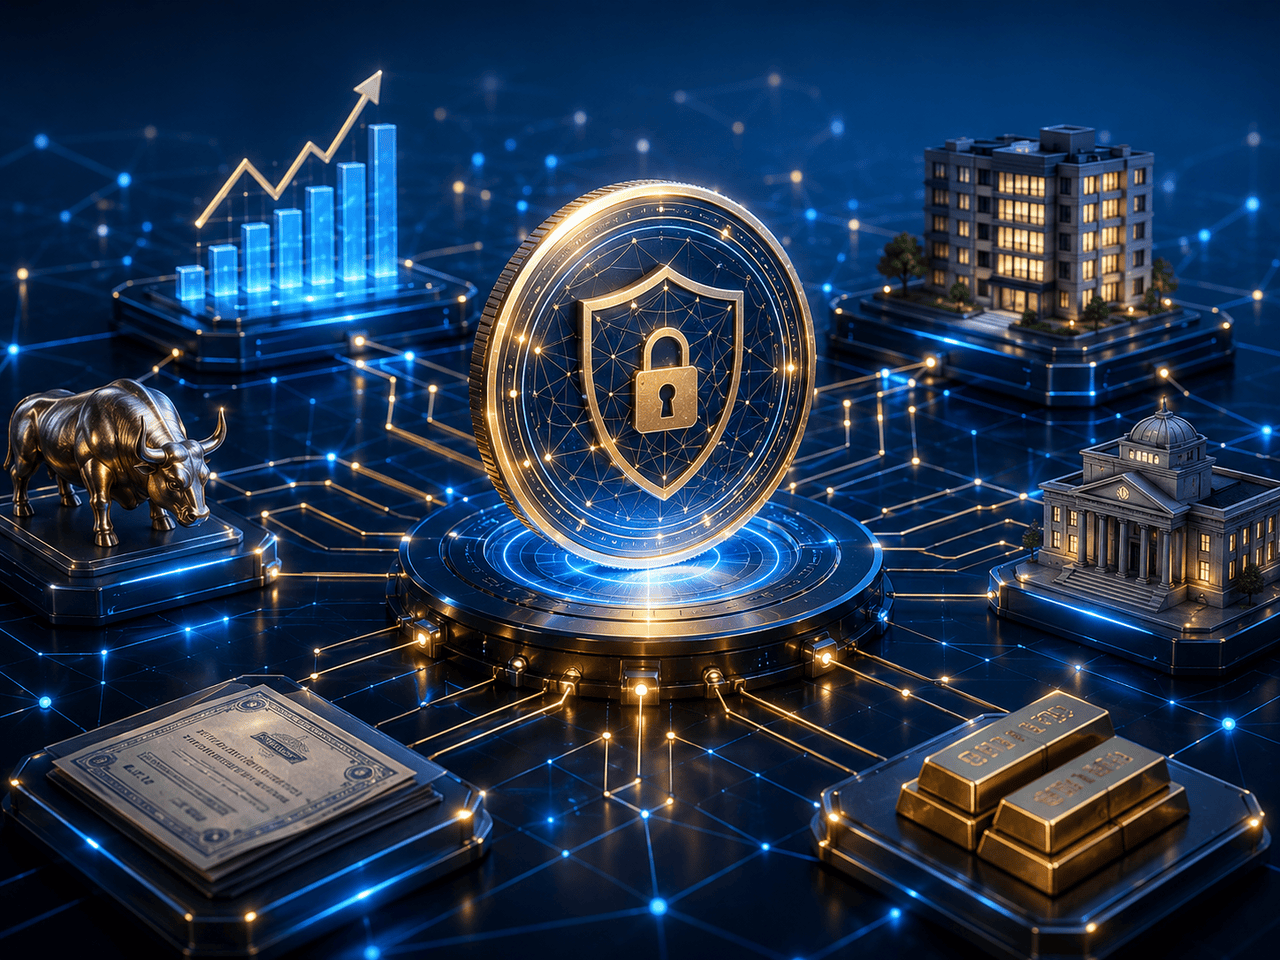
What is a security token? It sounds like a straightforward question, but the answer sits at the crossroads of traditional finance, blockchain technology, and securities law. Put simply, a security token is a digital token issued on a blockchain that represents a real-world financial asset. Think of it as a stock certificate or bond document, […]